Enterprise security in 2026 is shaped by several pressures arriving at once, each of which would strain a mature security organization on its own.
Ransomware chains now run for weeks before anyone notices. Identity governance built for human lifecycles is being asked to supervise agents that authenticate at machine speed and never sleep. Regulators have moved past asking what data you hold. Tool sprawl produces alert fatigue and integration gaps, and the talent market cannot supply expertise fast enough to close them.
Those look like five separate problems. They share a location.
Network and endpoint security do not protect the browser because neither was built to see inside a session. Network security secures the pipe. Endpoint security secures the machine. What happens between those two points, inside the browser session itself, falls outside both.
That gap is where employees work, where AI agents operate, where data moves between sanctioned and unsanctioned tools, and where most attacks now arrive.
“The browser is not one more place for enterprise risk. It is the only place where all of the things keeping you up at night are happening at the same time.”
Ransomware chains begin in the browser, long before the ransom note appears. By the time an event becomes visible, the damage is done.
Today’s attack chains are prolonged and deliberate. Credentials are compromised, infrastructure is mapped, and data is exfiltrated, all before a single file is encrypted. The ransom is the final step in a process that may have been running for weeks.
Those chains start with a user being convinced to take an action that opens the door. Threat actors build malicious sites, run phishing and social engineering campaigns, and serve malvertising. AI tools now let them create and iterate on convincing exploits faster than ever. The browser session where that initial access happens sits outside the view of conventional security tools.
That has a specific consequence for the CISO. Ransomware events increasingly become regulatory events. The board and the general counsel then ask whether the organization had visibility into how the chain began.
Every browser session is an identity event because a human or an agent asserts credentials, accesses an application, and transacts with data. Identity governance frameworks were built to manage access at the network perimeter and the application layer, not to see inside an active session.
The gap widens considerably for non-human identities. Agents operating through web interfaces authenticate and execute transactions at machine speed and high volume. Governance built around human lifecycle events and periodic access reviews was never designed to oversee that. Those agents frequently carry privileges granted without the scoping and recertification applied to human access.
When an over-privileged agent is compromised, the blast radius can extend well beyond its immediate system, reaching connected and third-party environments the organization does not directly control. The browser is where that identity exposure is most frequently exploited and least effectively governed.
Network logs cannot prove compliance because they record that a connection was made, not what happened inside it.
Regulatory requirements have moved beyond data inventory. GDPR, HIPAA, SEC disclosure rules, and emerging AI governance frameworks increasingly require organizations to demonstrate how data was accessed, by whom, and what was done with it.
That requirement runs directly through the browser, and network logs cannot answer it. They cannot record what was read, copied, pasted, or submitted within a session. For most enterprises the browser session, where regulated data is most actively touched, is the least instrumented point in the entire compliance architecture. That gap is a liability waiting for an audit.
Closing the browser gap works through consolidation rather than addition, because every tool you add compounds the complexity that created the gap in the first place.
Security teams are already managing alert volumes that outpace analyst capacity and integrations that create as many gaps as they close. Tool sprawl and talent scarcity trace back to the same root cause. Every additional tool is another integration to maintain, another alert queue to manage, and another domain of expertise to staff.
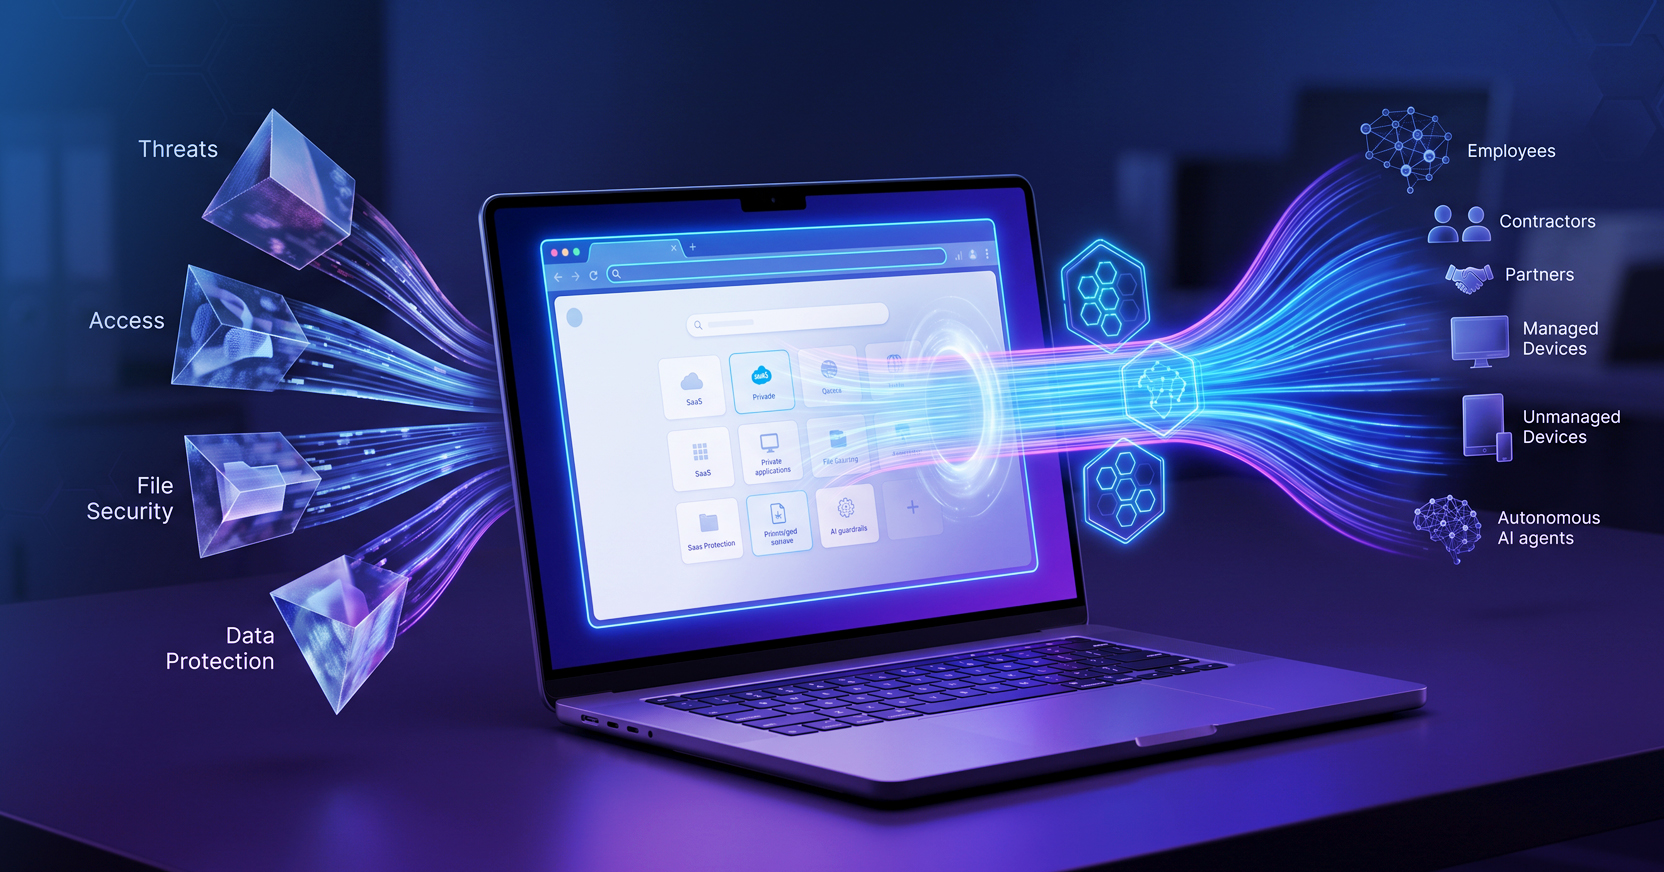
Consolidating threat prevention, file security, data protection, access governance, and session visibility into a single browser-based layer addresses both constraints at once. Fewer tools means fewer integrations and fewer gaps. The Menlo Browser Security Platform is built on that premise, and the Menlo Secure Enterprise Browser governs every session, human or agent, from one control point.
Closing the gap means adding visibility and control at the layer where the stack currently ends, which an existing architecture can absorb without a rebuild.
Browser security has become foundational to the security program rather than an optional addition to it, because the browser session is where the program’s other layers stop.
The five pressures described at the top of this piece are one problem appearing in several places, all connected by the browser. Ransomware chains begin there. Identity events, AI agent activity, and the movement of regulated data all run through the same session.
And the tools meant to secure everything else stop at the browser’s edge.
“The browser isn’t one more surface to secure. It’s the surface.”
What Is the Browser Security Gap?
It is the space between where network and endpoint security stop and where work actually happens. Network security secures the pipe and endpoint security secures the machine, but neither protects what happens inside the browser session itself.
Why Don’t Existing Tools Catch Browser-Based Attacks?
Because they see the connection rather than the content. Conventional tools inspect traffic on its way to the browser and monitor the device it runs on. The user action inside the session, which is what attackers are actually engineering for, is outside both views.
How Does the Browser Relate to Ransomware?
It is where the chain begins. Phishing, social engineering, and malvertising are all designed to trigger an action inside a browser session. The encryption event at the end may be weeks later, after credentials have been compromised and data already exfiltrated.
Why Do Compliance Frameworks Care About the Browser?
Because regulators now ask how data was accessed and what was done with it, not simply what data you hold. Network logs cannot answer that. The browser session is where regulated data is most actively touched and least instrumented.
Does Fixing This Mean Replacing Our Security Stack?
No. It means adding visibility and control at the layer where the existing stack ends. Consolidating browser-layer functions into one platform also reduces the integration and staffing overhead that point solutions create.
Why Is a Single Control Point Better Than Dedicated Tools?
Because every additional tool is another integration to maintain, another alert queue, and another domain of expertise to staff. Consolidating browser-layer security means one architecture covering the surface where most risk now lives.
About the Author
Sameep Gidda is a Digital Marketing Campaigns Specialist at Menlo Security. Focused on GEO strategy, content marketing, and AI visibility, Sameep works to ensure Menlo’s expertise in browser security and agentic AI reaches the security professionals who need it most.
This article draws on The CISO’s Guide to Secure Enterprise Browsers. Download the Full Guide for the complete picture.
Ready to see it in practice? Schedule a Demo Here.
Menlo Security