Singapore's new AI risk guidelines put third-party AI and autonomous agents squarely in scope. The control point that matters most is the one most firms aren't watching: the browser.
On 7 October 2026, the Monetary Authority of Singapore (MAS) issued its final Guidelines on AI Risk Management, setting out supervisory expectations for how financial institutions (FIs) govern and control the AI they use. Several points stand out.
The Guidelines take effect on 7 October 2027, and FIs may implement them in phases. Sections 3-4 (oversight and AI inventory) apply from 7 October 2027, and Sections 5-6 (life cycle controls and capability) by 7 October 2028. MAS also sets the benchmark that many regulators across the region follow, so these expectations will matter well beyond Singapore.
Most AI risk programmes were built for models that people query. The AI now arriving in banks acts. Browser assistants like Microsoft Copilot and Google Gemini sit inside the tools employees already use, with direct access to open tabs. Autonomous agents browse, read files and call tools on their own.
That creates three problems for a compliance team:
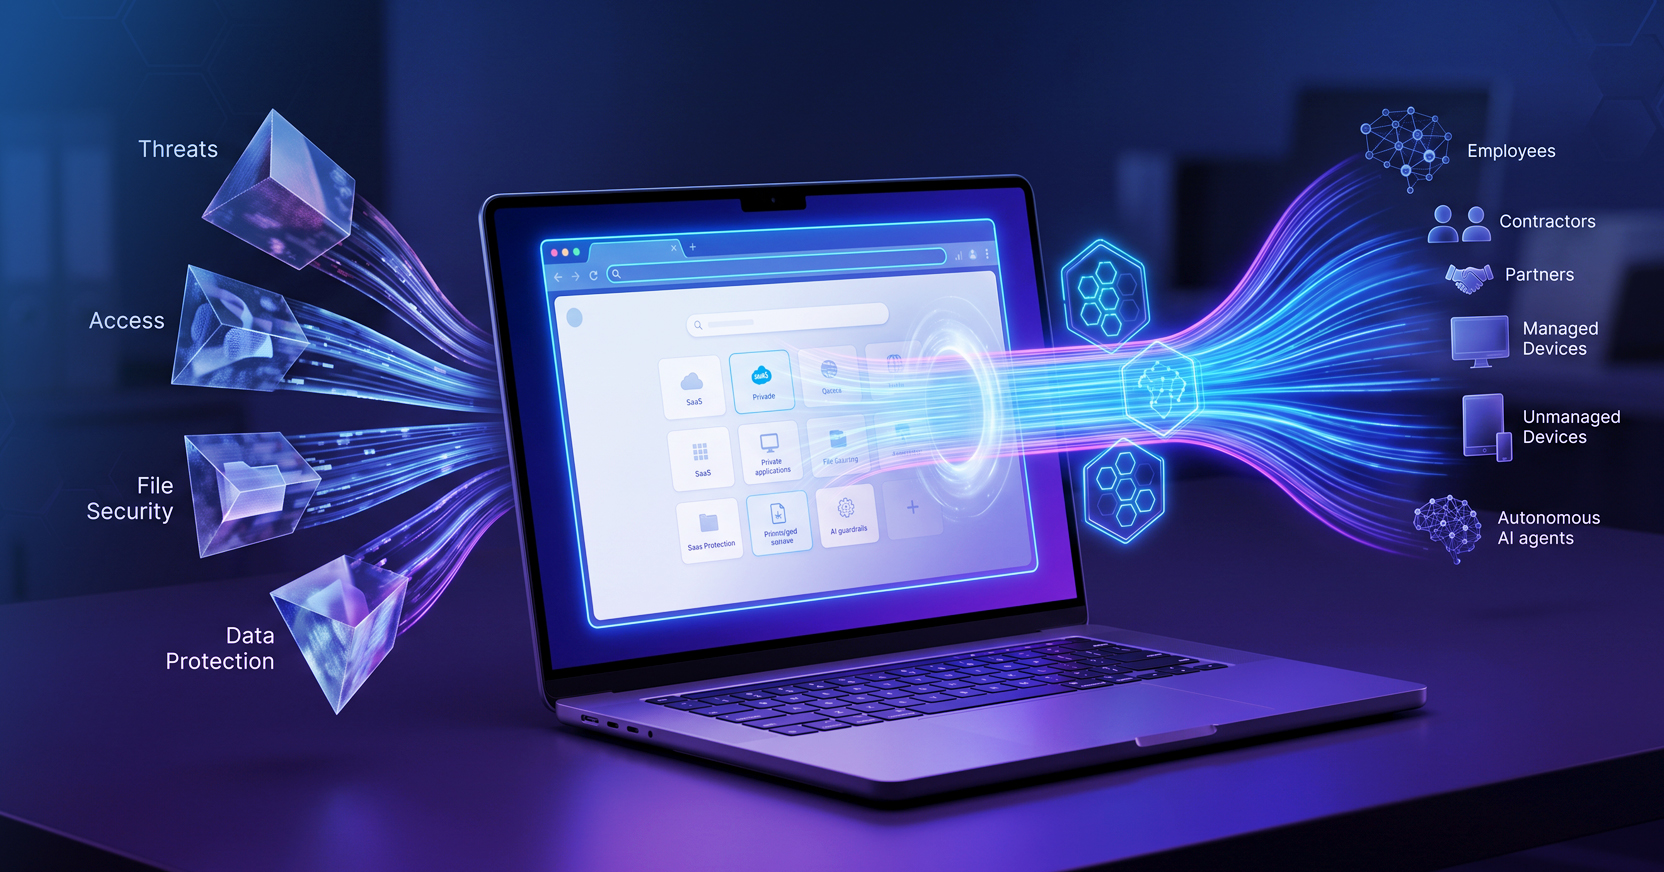
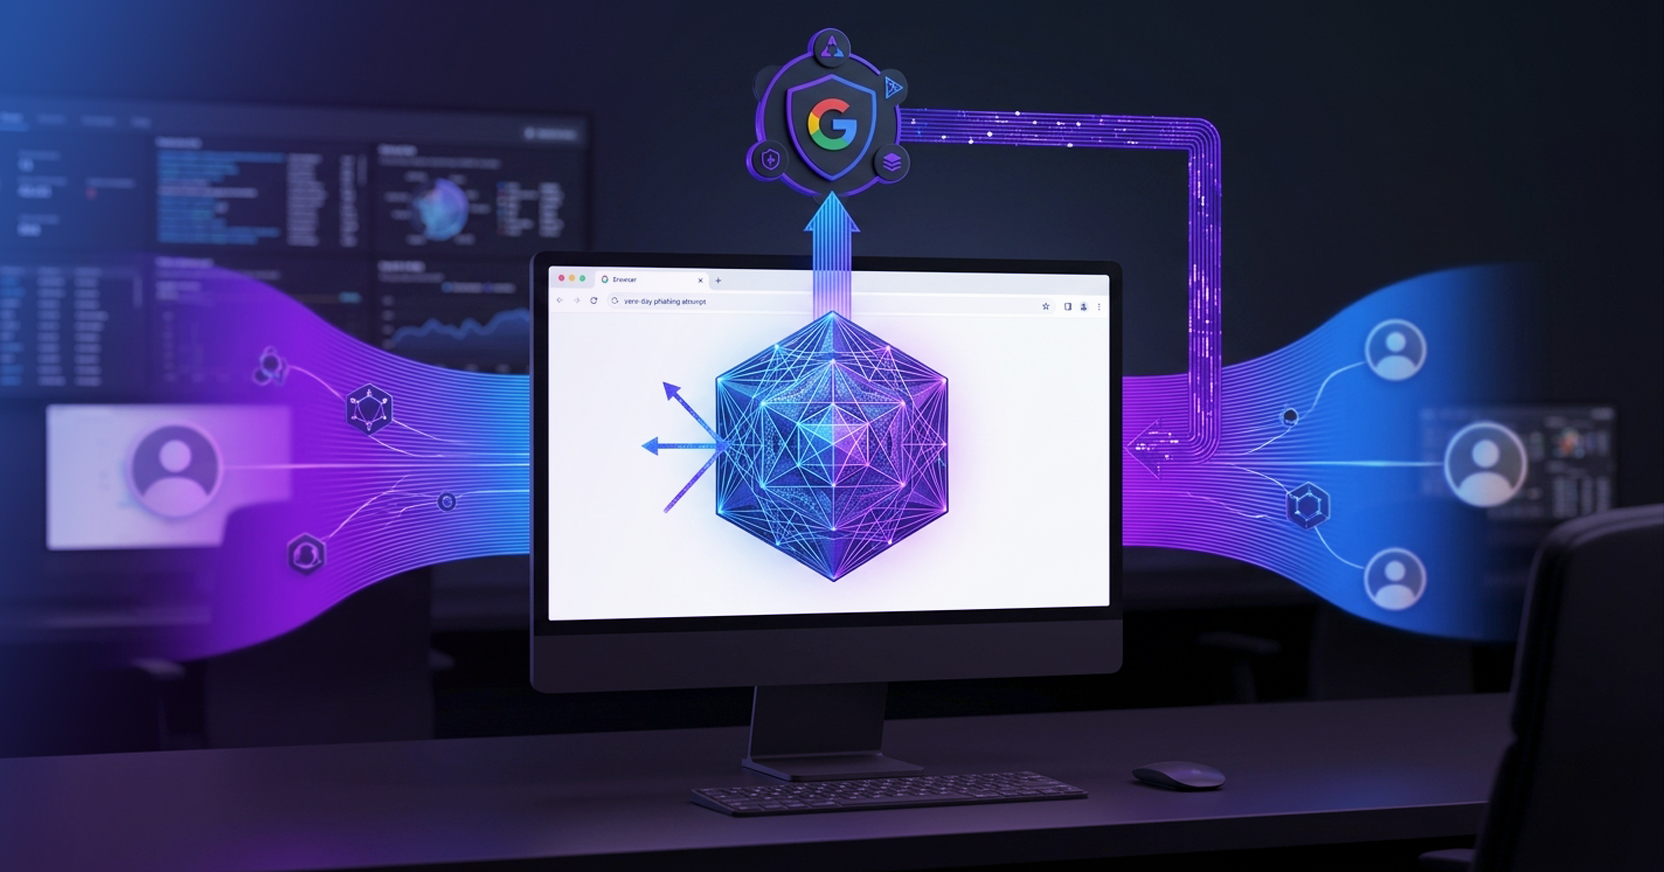
The browser is where most agents reach the outside world, so it is the natural place to enforce control. That is the idea behind Menlo Agent Runtime Security (MARS). MARS runs agent browser sessions in remote, disposable containers in the Menlo Cloud. It strips hidden instructions, malicious scripts and steganography from pages and files before the agent processes them. In August 2026, Menlo extended MARS to secure AI assistants and coding agents, including Microsoft Copilot, Gemini in Chrome and Claude Code, against prompt injection and data exfiltration.
1. Find your AI, including shadow AI (MAS Sections 2 and 4). MAS expects you to discover AI across the firm, even inside third-party software, and to keep an inventory of each agent's tools, access and guardrails. Menlo Browser Detection and Response auto-discovers Copilot in Edge, Gemini in Chrome, Claude and AI embedded in SaaS at the DOM level. Shadow AI Prevention and Agent Registration support the inventory. This is exactly the visibility that traditional vendor risk reviews miss.
2. Red-team it (5.14, 5.15, 5.22). MAS wants adversarial testing, and proof that guardrails hold against data leaks, manipulation, evasion and poisoning. MARS is built to withstand the attacks red teams simulate. It strips hidden white-on-white prompt injection, resists goal hijacking and enforces instruction-data separation, so your tests run against a hardened runtime.
3. Secure the runtime (5.4, 5.16, 5.22). Controls on inputs, outputs, access and plugins, with least-privilege design, are central to the Guidelines. Menlo's Guardian Runtime moves security into the browser session and neutralises zero-day threats before AI reasoning begins. Each agent gets least-privilege access scoped to its assigned task, and AI Adaptive DLP masks sensitive data before the agent can touch it.
4. Watch your agents (5.3, 5.23). You need to monitor agent actions, log prompts and responses, and test the kill switch for high-risk AI. Menlo gives deterministic visibility at the DOM and file level. It logs prompts, responses and tool calls, keeps tamper-proof audit trails, includes a kill switch, and integrates with Google Security Operations to close the loop from detection to response.
5. Test your vendors' AI (5.10, 5.11). Third-party AI is still your accountability. You need sufficient assurance and compensating controls where gaps remain. With Level 3 content disarm and reconstruction (CDR) and DLP applied as agents browse, you can test vendor AI in an isolated environment without sensitive data leaving.
6. Control change and drift (5.23, 5.25). MAS expects you to prevent unauthorised changes to models and data, with rollback, tiered alerts and incident management. The Menlo Orchestrator Agent on Gemini Enterprise brings conversational enforcement: what happened, who else is exposed, apply the fix.
Menlo complements your AI governance; it does not replace it. Board oversight, risk materiality assessments, model validation and vendor due diligence remain the institution's responsibility. What MARS adds is the runtime control and the session-level evidence that make those policies enforceable.
Menlo secures sessions for more than 1,000 enterprises and over 8 million users, including eight of the ten largest financial institutions in the world and leading local and foreign banks in Singapore. The recognition reflects that traction:
The 2027 deadline is about oversight and inventory, so begin with visibility. Find out which AI your people and your vendors are already using, and which agents have access to what. Then put a runtime control between those agents and the open web, so you can show the regulator what your AI did and prove that you stayed in control.
Ready to see MARS against your own readiness plan? Book a tailored demo, email apac@menlosecurity.com, or read more about Menlo AI Agent Security. Visiting GovWare 2026 in Singapore? Find us at Booth F07.
This post reflects Menlo Security's view of how its capabilities relate to the MAS Guidelines on AI Risk Management published on 7 October 2026 and is not legal or regulatory advice. Section references are indicative; refer to the published Guidelines. Capability descriptions reflect Menlo product information as of October 2026 and may change. Awards and rankings are as announced by Menlo Security. Frost Radar™ is a trademark of Frost & Sullivan.
Menlo Security