Menlo Closes the Loop on Zero-Day and AI Agent Attacks with New Google Security Operations Integration
Details


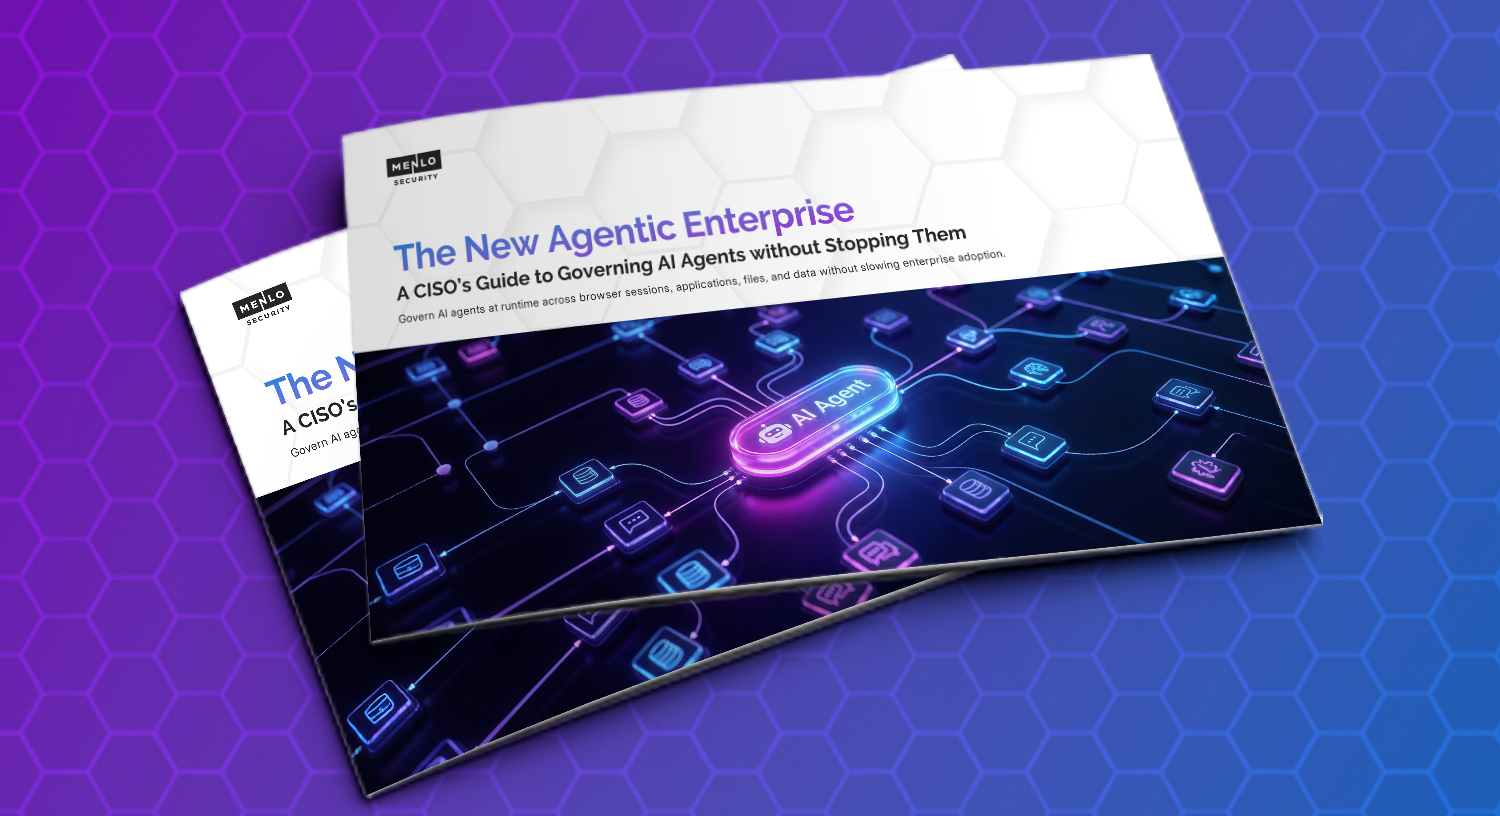
AI agents browse the web, retrieve files, call tools, and act on enterprise data with limited human involvement. OWASP (Open Worldwide Application Security Project) has formalized many of the risks posed by this shift in its guidance on LLM and agentic systems, including prompt injection, excessive agency, tool misuse, identity and privilege abuse, and sensitive information disclosure.
How MARS Neutralizes the Agentic Attack Surface, based on the OWASP GenAI LLM Top 10 2026, shows where risk emerges across the agent workflow and how Menlo Agent Runtime Security (MARS) enforces policy at runtime, outside the agent’s own reasoning, reducing the opportunity for malicious content to influence an agent and limit the consequences of unsafe behavior while preserving the autonomy that makes agents valuable.
In this eBook, you will learn:
Download the eBook to see how agents can introduce serious risks to the enterprise, and how MARS breaks the agentic attack chain.